How Preflex and Sonar sparked conversations on code quality, security, and the future of DevSecOps in India.
The Show in Numbers
A landmark edition that brought India's DevSecOps community together in the capital.
12th
Edition of the India DevOps Show, New Delhi
Being There as Sonar's Partner in India
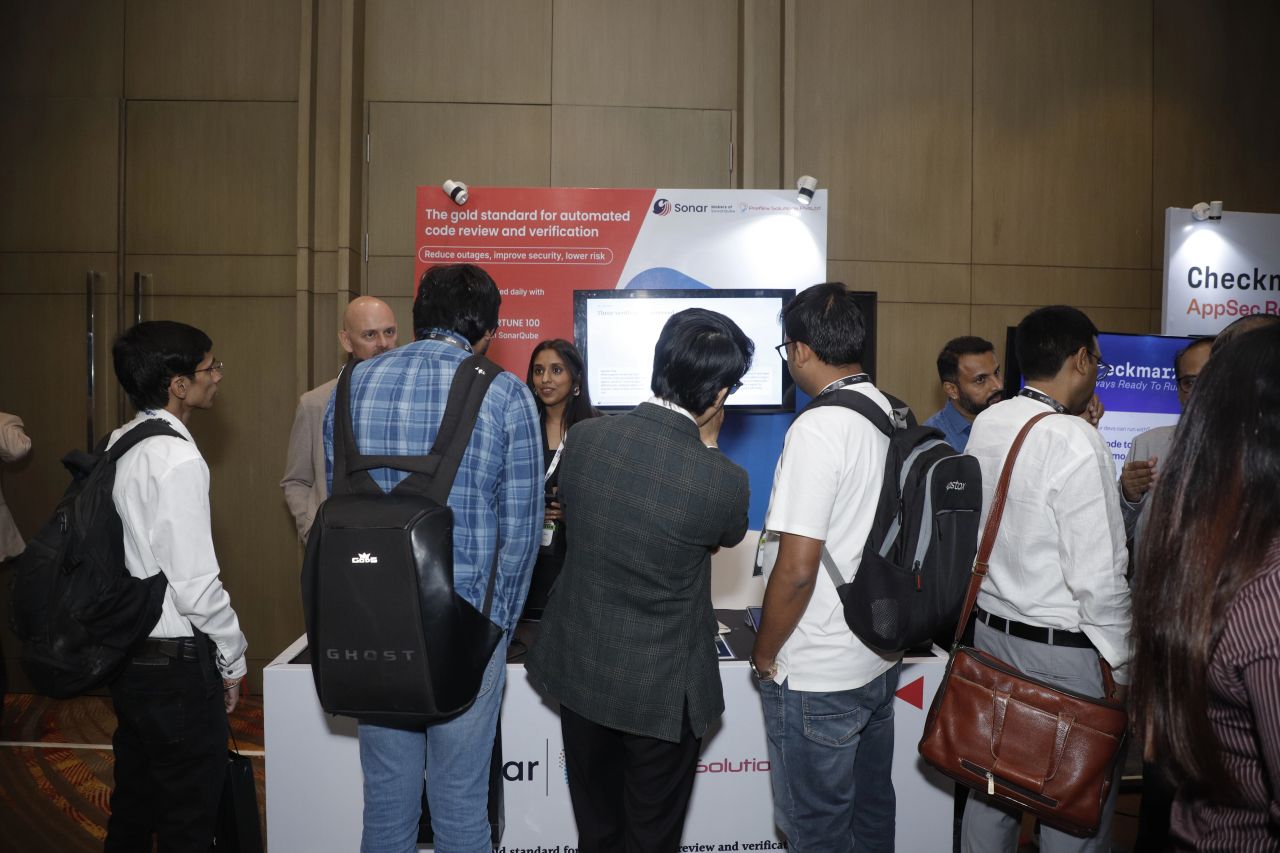
At the 12th India DevOps Show in New Delhi, Preflex Solutions represented Sonar on the show floor as its dedicated India partner — bringing the message of clean, secure code directly to the engineering and security leaders who need it most.
Our booth sparked real conversations: on code quality, on security built into pipelines, and on what it actually takes to ship clean code at scale in fast-moving engineering organisations. From BFSI teams managing compliance to product companies scaling their engineering, the appetite for automated code governance was unmistakable.
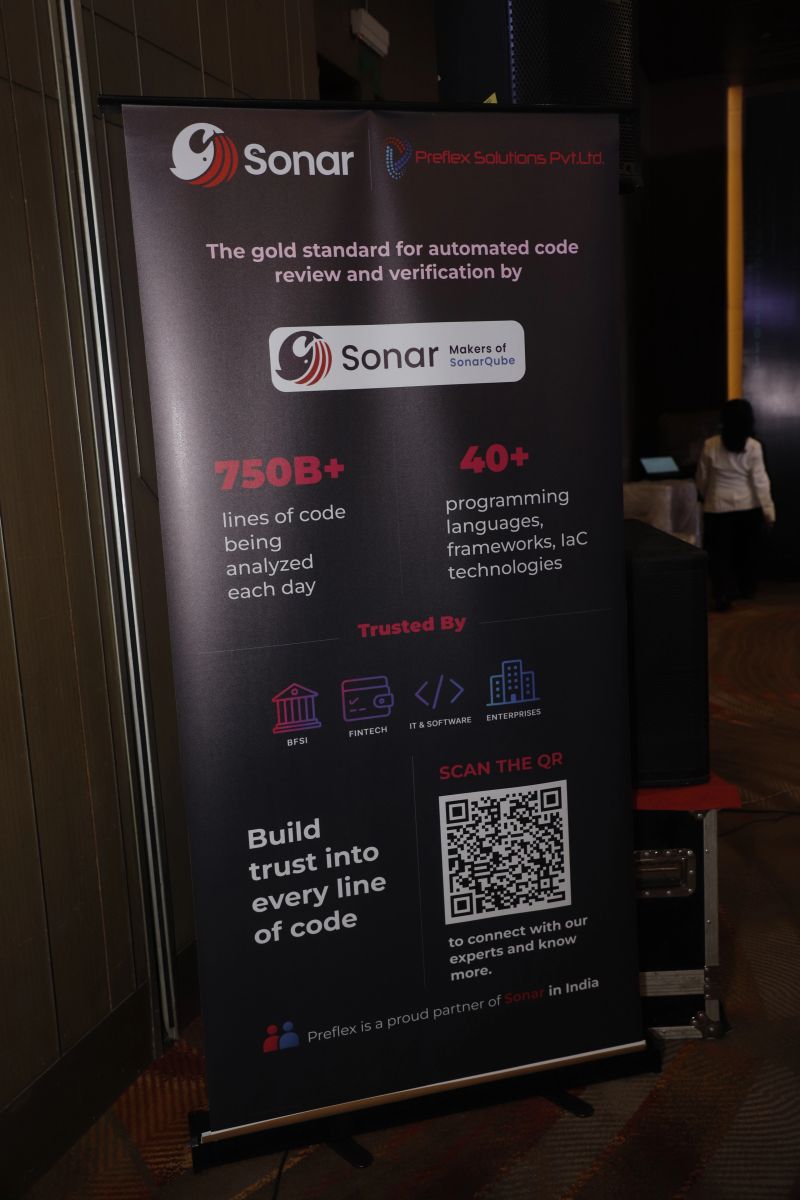
The standee said it best: “The gold standard for automated code review and verification” and “Build trust into every line of code.” Those lines resonated across every conversation we had.
“Code is moving faster than ever. Reviews and verification haven't kept up.”
AI Accelerates Code Quality Gates Haven't Scaled
AI is accelerating code output across engineering teams at a pace that manual review simply cannot match. The result: bugs slip through faster, technical debt accumulates silently, and security vulnerabilities get baked into production before anyone catches them.
SonarQube: Automated Quality Gates in CI/CD
SonarQube solves this with automated code review and security analysis embedded directly in your CI/CD pipeline. Every commit is analysed. Every vulnerability is caught before it ships. Quality and security become continuous, not an afterthought at the end of the sprint.
Who We Met and What They Needed
Trusted by BFSI, Fintech, IT & Software, and Enterprise teams across India.